The same data typed in twice
Orders from the website re-entered into billing, and payments copied from the bank portal into the ERP.
We design, build and document secure REST APIs and webhooks, and integrate your software with payment gateways, SMS and WhatsApp, logistics, GST and partner platforms. Clear contracts, proper authentication and monitoring, from engineers who have built integration-heavy platforms for 21 years.
Signs you need better APIs
When systems can't talk to each other, people become the integration layer: copying, re-keying and chasing mismatches. Good APIs remove that work for good.
Orders from the website re-entered into billing, and payments copied from the bank portal into the ERP.
Distributors, marketplaces and enterprise customers want to connect directly, and spreadsheets by email no longer satisfy them.
A third-party change or a timeout breaks the link, and nobody notices until a customer complains days later.
Payment gateway callbacks are missed or handled twice, leaving orders, wallets and accounts out of step.
API keys hard-coded in apps, no rate limits and endpoints that return far more data than the caller needs.
Only the developer who wrote the API knows how it works, so every new app or partner takes weeks to connect.
API development & integration services
We build new APIs for your products and partners, and connect your systems to the Indian and global services your business depends on.
Resource design, versioning, pagination and error handling, specified in OpenAPI before the first endpoint is coded.
Read more about Custom REST API DevelopmentReal-time events between systems, with signatures, retries and idempotency so nothing is lost or duplicated.
Razorpay, PayU, Cashfree, Stripe and UPI, with reliable callbacks, refunds and daily reconciliation.
Read more about Payment Gateway & UPI IntegrationOTPs, alerts and notifications through DLT-registered SMS, the WhatsApp Business Platform and transactional email.
Courier and shipping APIs, address lookup, live location tracking and route data in your apps.
Read more about Logistics, Maps & GPS IntegrationGST e-invoice and e-way bill APIs, Tally Prime synchronisation and bank statement imports.
OAuth 2.0, JWT, API keys, scopes, rate limiting and audit logs for every client that calls your API.
Read more about API Security & Access ControlSecure API layers over older applications and databases, so modern apps can use them safely.
Read more about Legacy System & Database APIsFast, versioned APIs designed for Android, iPhone and Flutter apps, with push notifications and offline sync.
Read more about Mobile App Back-End APIs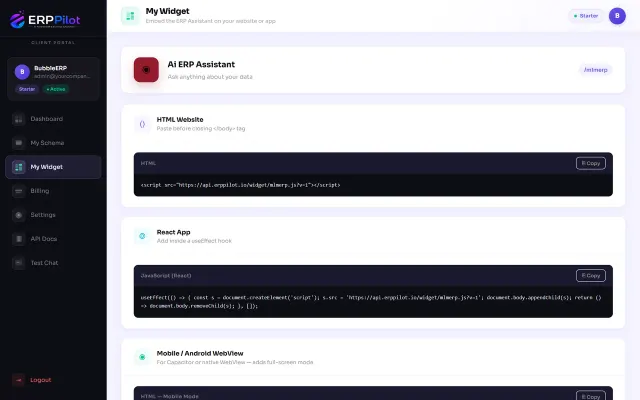
API design & documentation
We agree the API contract before writing code: resources, request and response formats, errors and versioning, all described in an OpenAPI specification. Your developers and partners can review it, generate client code and test against a sandbox while we build, and the documentation stays in step with every release.
Payment & transaction APIs
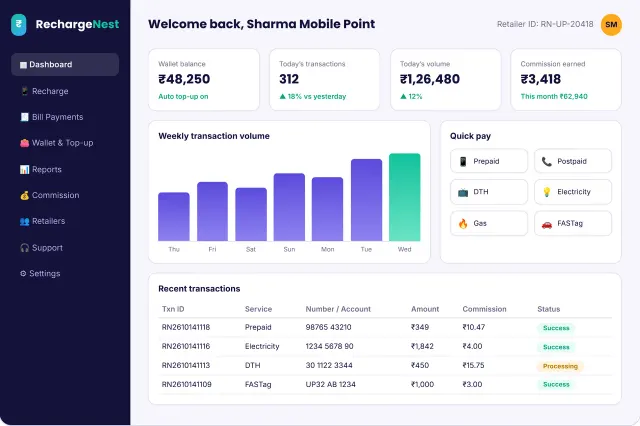
Payment integration is easy to demo and hard to get right. We handle the details that matter in production: verifying gateway signatures, processing callbacks exactly once, retrying failed notifications, handling refunds and partial captures, and reconciling every transaction against the settlement report.
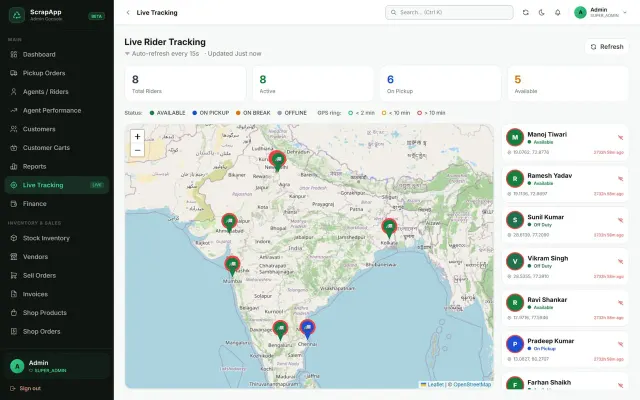
Logistics, maps & location APIs
For delivery, field-service and logistics businesses, we connect courier and shipping platforms, maps and GPS feeds so your apps show where every order and every rider is. Location updates stream from mobile apps through our APIs to admin dashboards in near real time.
API security & access control
An API is a door into your business data, so we treat its security as a design requirement. Each client gets its own credentials and scopes, traffic is rate-limited per key, and every call is logged. We follow the OWASP API Security Top 10 and test for broken authorisation before go-live.
Legacy system & database APIs
Replacing a working legacy system is often unnecessary. We wrap it with a secure API layer instead, reading from and writing to its database or interfaces in a controlled way, so new web apps, mobile apps, AI tools and partners can use its data without touching the original code.
What you get
Every API development project ends with a production-ready interface and everything your developers and partners need to rely on it.
Last 30 days
Integration plan
Our API development process
Contract first, tests throughout and monitoring from day one, with a fixed, itemised quote once the contract is agreed.
We review the systems and third-party services involved and confirm what can be integrated, and how.
Resources, payloads, errors, authentication and versioning agreed in an OpenAPI specification.
Endpoints, webhooks and integrations developed with unit, contract and end-to-end tests.
OWASP API checks, load testing and a sandbox so your apps and partners can integrate safely.
Production release with uptime, latency and error monitoring, alerts and a versioning plan.
Engagement models
Whether you need a payment gateway connected this month or a partner API programme, the scope and price are agreed before we start.
Free
A quick technical review of what you want to connect.
Fixed price
One third-party service connected properly.
Fixed price
A complete API for your apps, partners or customers.
Monthly retainer
Keep integrations healthy as providers change.
Why Sysfo
Our own platforms depend on payment, recharge, SMS, mapping and AI APIs every day, so we know how integrations fail in production and how to design them so they don't.
We have built wallets, recharge and bill-payment flows where every callback and refund must reconcile exactly.
UPI, Indian payment gateways, DLT SMS, GST e-invoice, e-way bill and Tally are familiar territory, not research projects.
Every API ships with an OpenAPI spec, interactive docs and samples, so your partners can connect without us.
Authentication, scopes, rate limits and logging follow OWASP API Security guidance from the first endpoint.
Uptime, latency and error alerts mean broken integrations are noticed in minutes, not when customers complain.
You own the code and the provider accounts. Secrets stay in your vault, and we sign an NDA on request.
FAQ
API development services cover designing, building, securing, documenting and running application programming interfaces. At Sysfo that includes custom REST APIs and webhooks, integration with third-party services such as payment gateways, SMS, WhatsApp, courier and GST platforms, API layers over legacy systems, authentication and rate limiting, OpenAPI documentation, sandbox environments and ongoing monitoring.
It depends on the number of endpoints and integrations, the complexity of the business rules, and the security and performance requirements. A single third-party integration is a much smaller job than a partner API platform. After a free feasibility check and contract design, Sysfo gives a fixed, itemised quote, so the cost is clear before development starts.
A standard payment gateway or UPI integration usually takes one to three weeks, including callback handling, refunds, testing in the provider's sandbox and going live. Timelines depend partly on the gateway's own account activation and approval process, which we help you complete in parallel with development.
REST is the right default for most business APIs and partner integrations: it is simple, cache-friendly and universally understood. GraphQL suits products where many different screens need flexible combinations of data, such as complex mobile apps. As part of our API development services we recommend the approach that fits your clients, and can offer both.
We authenticate every caller with OAuth 2.0, JWT or per-client API keys, check permissions on every object requested, validate all input, and apply rate limits and quotas per client. Traffic is encrypted with TLS, secrets are stored in a vault, and every call is logged. We test against the OWASP API Security Top 10 before go-live.
Usually, yes. If the legacy application has a database we can access safely, we build a secure API layer that reads and writes through controlled endpoints, exposing only approved tables and fields. This lets new web apps, mobile apps and partners use the data without rewriting the original system.
Yes. Every API we build comes with an OpenAPI specification, interactive documentation, a Postman collection, code samples and a sandbox with test credentials. Partners can integrate on their own without waiting for our developers, and the documentation is generated from the code, so it is updated automatically with each release and never drifts out of date.
Providers regularly update or retire API versions. Under an API care retainer we track provider announcements, test changes in sandbox, update your integration before the deadline and monitor it in production. Monitoring and alerts also catch unexpected changes quickly, so failures are fixed in hours rather than discovered days later.
You do. The source code is delivered to your own repository, and payment, SMS and other provider accounts are registered in your company's name. Credentials stay in your secrets vault rather than in our systems, and we sign an NDA on request. You are free to maintain the API yourself or with any other vendor.
Plan your integration
List the systems, partners or third-party services involved. An integration engineer will reply within one business day with a free feasibility check and the next steps.